For CISOs, security architects and their teams
Fewer pitches. Solutions that fit.
You do not need another vendor meeting. You need the right solution, checked against your architecture and your compliance requirements, by people who understand both. That is what we do.
Sound familiar?
If you run security for a company in the German-speaking market, you probably know these situations:
- Your inbox is full of vendor outreach, and very little of it has anything to do with your actual problem.
- A demo looks great, and three months later procurement finds out where the data is really processed.
- Every vendor claims to cover everything, so comparing them takes longer than the project itself.
- Events turn into sales pitches, and the conversations you came for happen in the hallway.
- You know strong European alternatives exist, but finding and vetting them is a project of its own.
We built Crossing Waters around the opposite.
What we do for security teams
Handpicked, not pushed
We work with a small number of vendors whose products we have looked at in depth, and many vendors who approach us do not make the cut. We never represent two vendors competing for the same shortlist.
Compliance checked upfront
Before a solution reaches you, we check it against the questions your compliance and procurement teams will ask in Germany, Austria and Switzerland: data protection, data residency, NIS2, the Cyber Resilience Act, the EU AI Act and certifications. So one conversation is enough to see whether it fits.
European solutions
We actively look for strong European vendors, for data residency, digital sovereignty and supply chains you can explain to your board.
Technical depth
We look at architecture, integration and day-to-day operations, not just the feature list, and we bring the vendor’s technical experts to talk to your architects.
Focus
Tell us the problem. We come back with the few options worth your time, or with an honest “nothing fits right now”.
Events without fluff
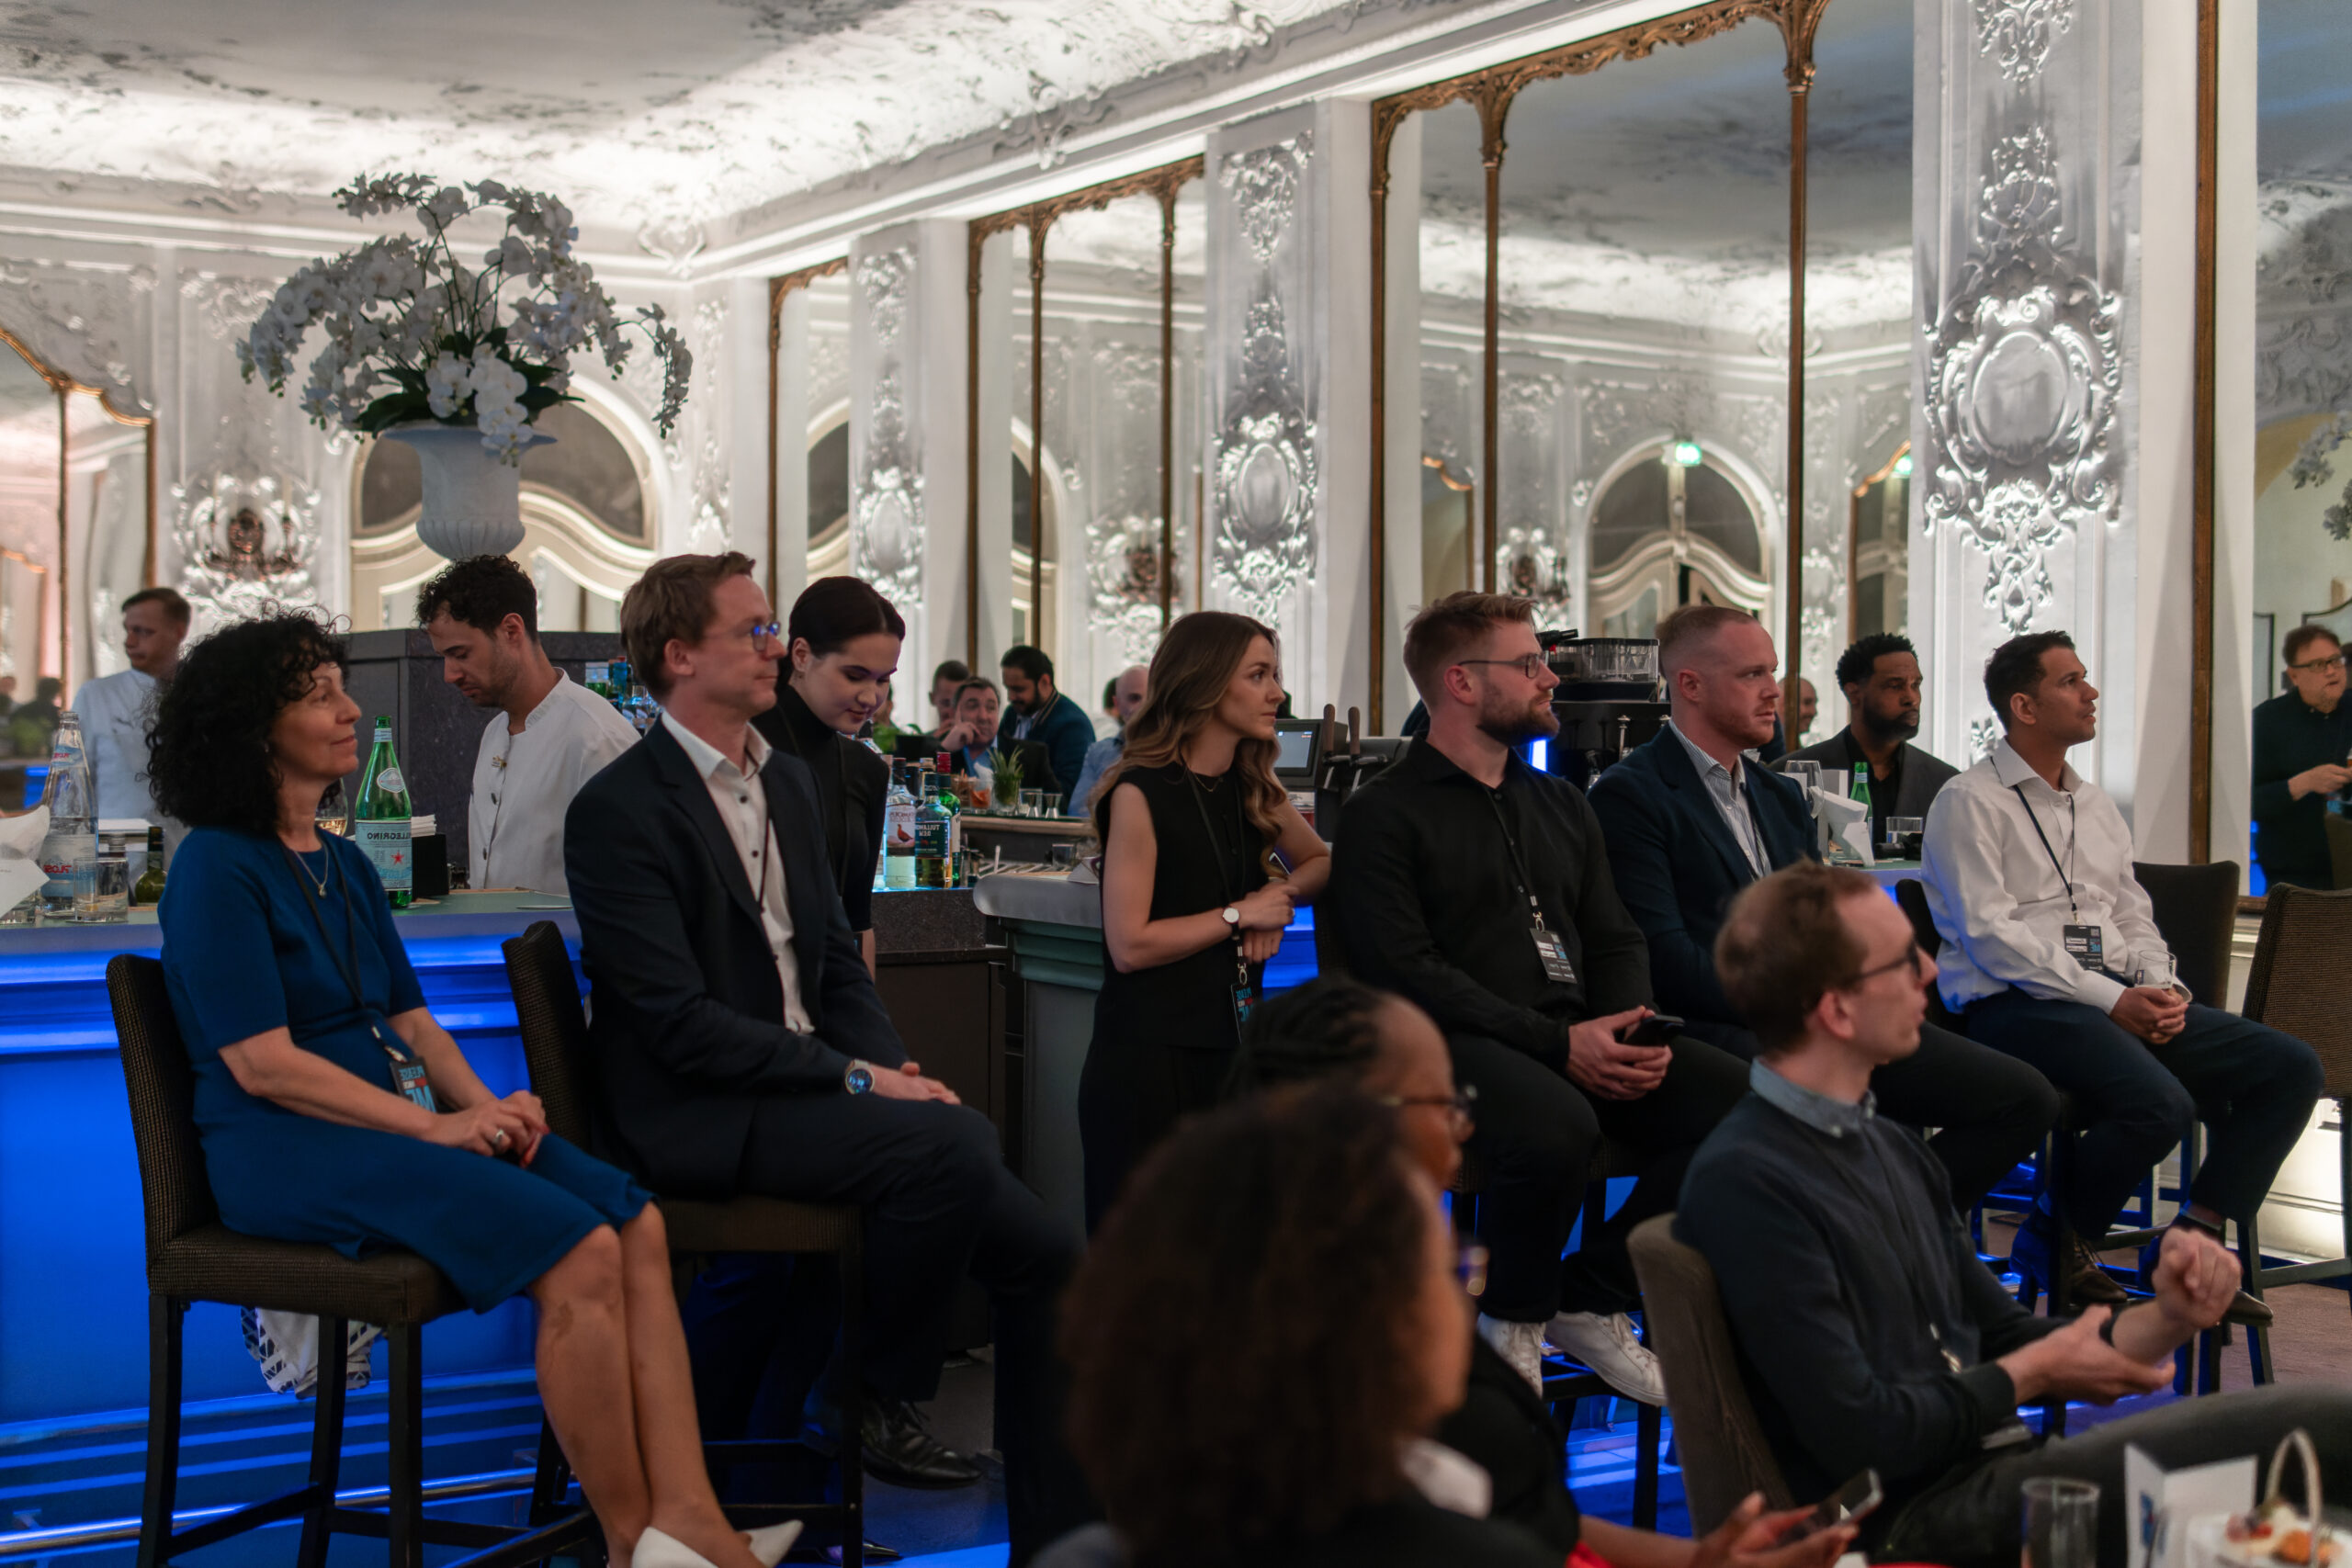
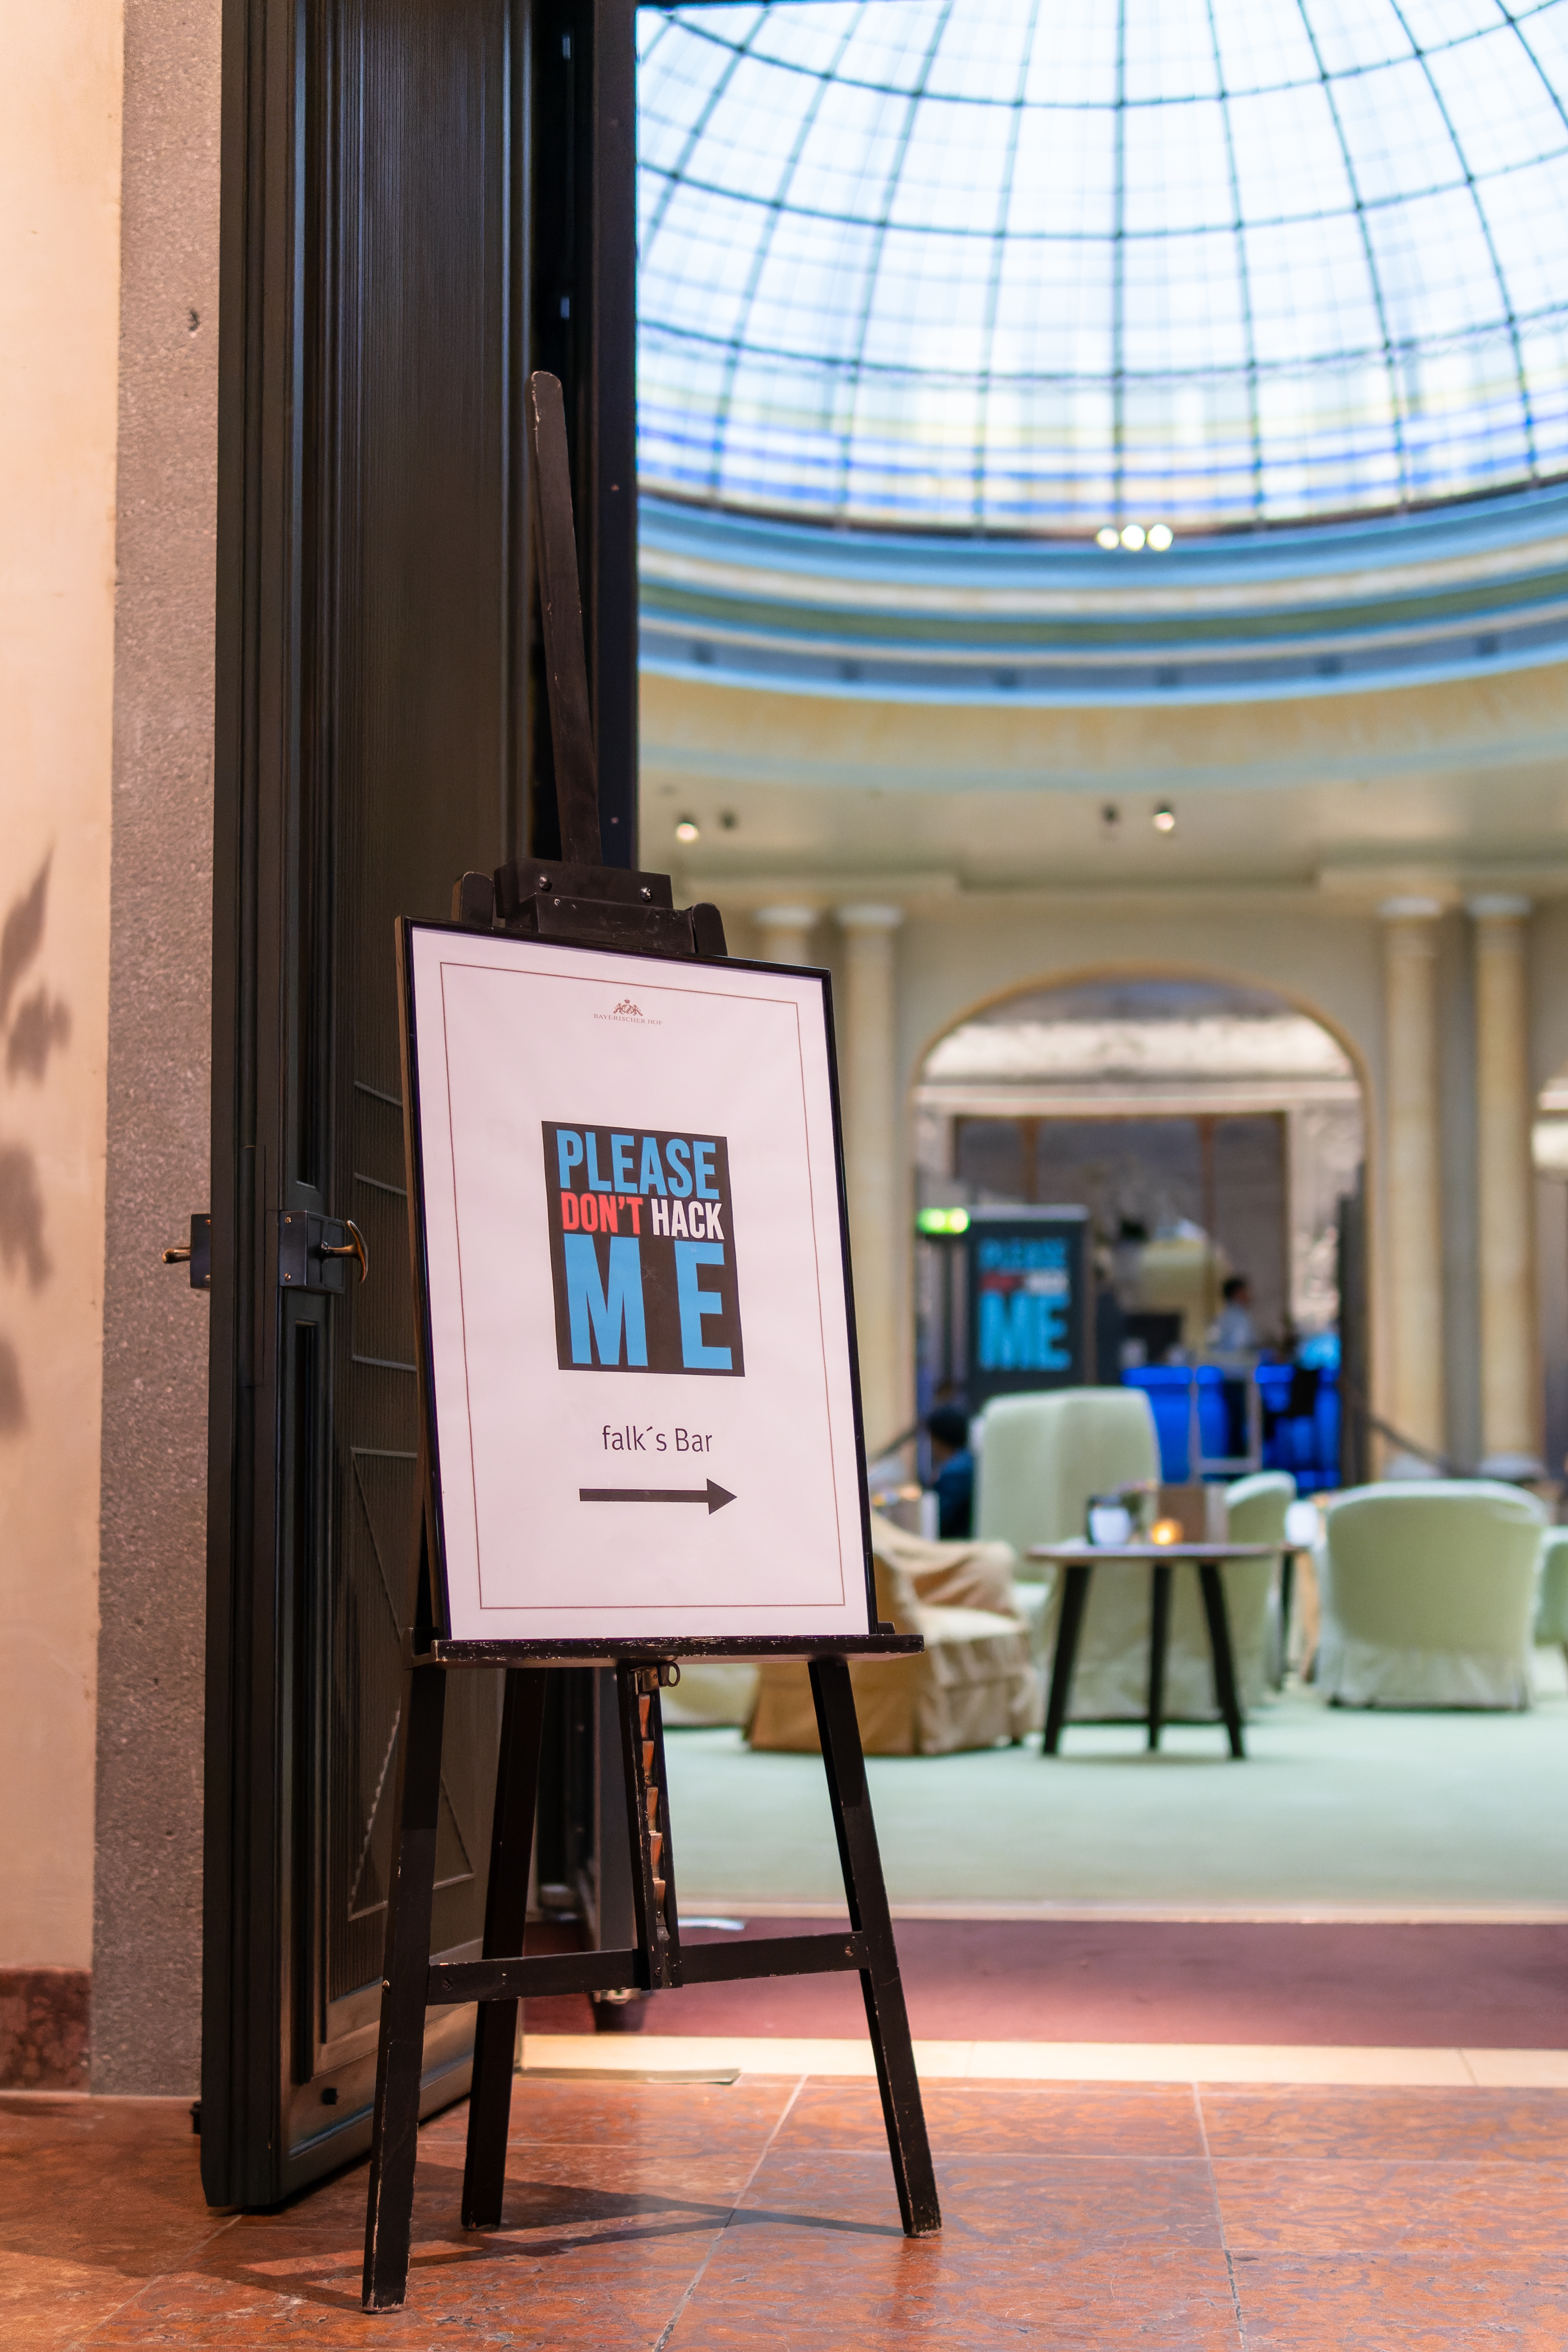
Our co-founder Felix Rosbach co-founded Please Don’t Hack Me: no pitches, no slides, just security leaders talking openly. We also host small breakfasts where peers share what actually worked.
How it works
1. Tell us what you need to solve
A short, confidential conversation about the problem, your environment and your constraints.
2. We check the fit
Technical, compliance and commercial, before anything reaches your desk.
3. A short list or an honest no
Only the options worth your time, with the reasons why.
4. Technical deep-dive on your terms
With the vendor’s technical experts and your architects, at your pace.
No obligation, and no follow-up sequence in your inbox.
Our promise to security teams
- We only bring solutions we would stand behind ourselves.
- We tell you when something does not fit.
- No competing vendors on the same shortlist.
- What you share with us stays confidential.
- Where you want it, we work with your existing partners.
Frequently asked questions
Are you a reseller or a consultancy?
Neither in the classic sense. We work with a small number of cybersecurity vendors on their Go-To-Market in the German-speaking market, and we connect security leaders with the solutions that actually fit their problem.
Which vendors do you work with?
We share our current portfolio in a personal conversation, together with why we chose each vendor and where it fits and where it does not.
Do you only work with European vendors?
No. We work with vendors from Europe, the USA and the UK. But we actively look for strong European solutions, because data residency and digital sovereignty matter more and more to security leaders and their boards.
What exactly do you check before bringing a solution to us?
Architecture, integration and operations on the technical side, and on the compliance side the questions your team will ask anyway: data protection under the GDPR, where data is hosted and processed, NIS2, the Cyber Resilience Act, the EU AI Act, certifications and the security controls CISOs usually check.
Can we buy through our existing partner or reseller?
Where the vendor works with partners, we involve the partner you prefer.
How is this different from analyst reports?
Analyst reports compare categories. We look at your problem, your architecture and your compliance requirements, and we bring the vendor’s technical experts to talk to your architects.
Tell us what you need to solve
A short, confidential conversation. If we cannot help, we will say so.